Clari5

January 2017 Issue

Break-Filter-BubbleFinancial Fraud: Greatest Hits of 2016

2016 had a financial fraud being committed once every 15 seconds, compelling financial institutions to buckle up. The trend will continue through 2017 with newer, more innovative attempts. Imperative therefore to think innovatively to stay ahead of the game.Read More

Fraud-proofing Credit Cards

While credit cards have transformed purchase transactions, it has not been without growing vulnerabilities. Read how globalization is driving card fraud and how innovative real-time, cross-channel approach can combat the trend.Read More

ETDigital Finance: What’s Next?

A visual depiction of how digital finance is transforming transactions along with a snapshot of the change indicators.Read More

“Inside Job”

The next episode in the financial fraud thriller series based on Clari5 product use-case scenarios, co-produced and directed along with Banking Technology magazine. Read the previous episodes –

Ep 2: Blacklisted
Ep 1: Malafide Intentions​

Read More


A ‘Yin and Yang’ Approach to Growing Topline and Bottom-line

How To Monetize your Anti-Fraud Solution to Make Money for you

Yin and Yang blogsIn Chinese philosophy,   yin and yang (also yin-yang or yin yang, ‘dark-bright’) explains how seemingly opposite or contrary forces may actually be complementary, interconnected, and interdependent in the natural world.

This intriguing idea actually applies perfectly in the context of banking, if we were to see the yin as saving money (from losses) and the yang as making money (from sales).

The fundamental principle is that the very same investment in data analytics and real-time decisioning for detecting/preventing fraud can be monetized for earning more revenues.

Imagine an intelligent system that understands customers’ behavioral patterns to detect and prevent fraud is also creating precise personas for marketing teams to target.

This is because the same extreme real-time, context-aware logic/approach used to combat cross-channel fraud can also help enable intelligent, hyper-precise targeted and contextual customer engagements.

At the heart of the hypothesis lies the fact that banks have the ‘soul’ of the customer.

Customer flowBanking is the only industry where the entire life of the customer flows through it. A bank knows how much its customers earn, where they live, where they travel to, how much they spend, who’s part of the family, whether they own their home, even how much fuel they put in the car.

No other industry (not even telco or retail) has this very special privilege of having a 360 degree view of a customer’s life. Only banks have the advantage and ability to actually convert this ‘resident intel’ to their benefit.

A real-time, enterprise-wide, cross-channel fraud management solution requires that every banking transaction is available in memory in real-time.

But since only a relatively small percentage of transactions are fraudulent and since the data is available in the system memory, the bank can run positive scenarios in real-time after having assigned fraud risk to certain transactions during the negative-scenario test-run.

Absolute real-timeThe solution can use the same data captured per transaction and analyze the spending and behavior patterns to throw up potential cross-sell and up-sell scenarios in absolute real-time.

Precise data analytics on behavior patterns helps create intelligent and efficiently targeted customer interactions and campaigns to grow the topline.

So while the solution helps the bank’s larger enterprise fraud management initiatives with …

  • A unified case management system for fraud/AML investigation with 360-degree view of behavior across products and channels in one single place.
  • Extreme real-time, context-aware, cross-channel fraud detection and prevention.
  • Monitoring financial and non-financial transactions of customers, accounts, users and employees across branch and channel transactions in real-time to detect suspicious fraud and respond with the right decision in real-time and generate alerts for investigation.
  • Monitoring Salary Accounts’ to identify increase in Salary Credits or non-usage of Salary Accounts.

… it can also be used for –

  • Tracking customers’ POS/E-com channels transactions for generating extreme real-time, as-of-the-moment cross-sell and up-sell alerts.
  • Identifying customers who usually travel internationally and offering them custom products in real-time.
  • Creating customer delight in branch and digital transactions.

So altogether the bank benefits from a –

  • Smart, intelligent, extreme real-time solution that manages fraud detection/prevention as well as enables customer revenue maximization.
  • Non-invasive, bolt-on solution that integrates seamlessly with source systems and reduces TCO.
  • Lowered cost of compliance of fraud and AML regulatory requirements.
  • Single, unified platform that helps protects the bottom-line and grows topline.

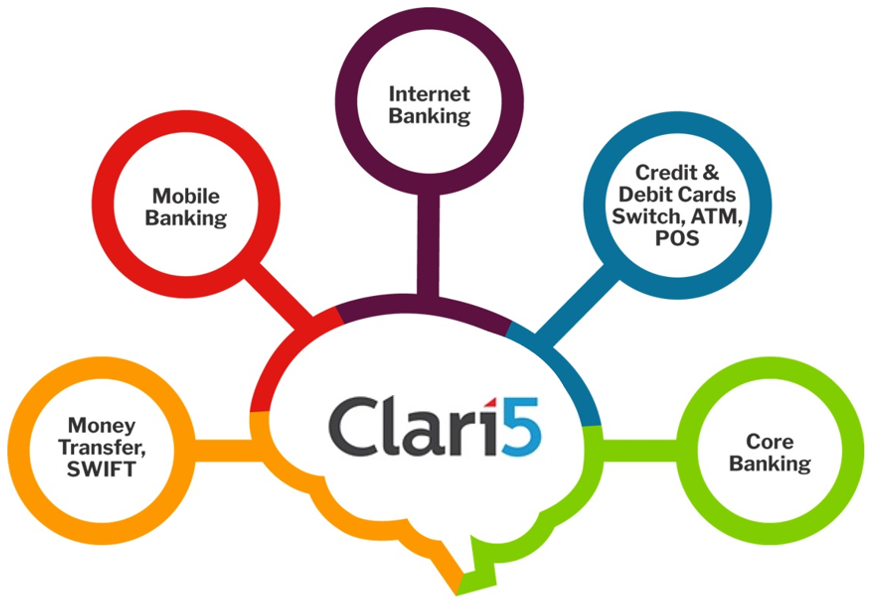
Unified Fraud ManagementWhile there may not be many solutions that have the ability to see topline and bottom-line as 2 sides of the same coin, CustomerXPs’ Clari5 seems to one. Its unified fraud management platform leverages the same context-aware, real-time decisioning to enable real-time customer cross/upsell.

Clari5 handles exceptionally large data volumes across multiple channels and source systems in real-time, and processes transactional as well as non-transactional events in real-time and applies over 150 rules to generate alerts in real-time that can be leveraged for both fraud management as well as revenue enhancement.

Banks get to use the same real-time insights that helps combat fraud to also generate profits because the approach that uses the same fundamental logic to protect/save money (curb fraud losses) is also being used to make money (upsell / cross sell).

If banks can view their topline and bottom-line as the yin and yang of their operations, then a single solution that helps achieve both can very well be the proverbial one stone designed to kill two birds.

Episode 3: Inside Job

Our new series of thrillers – produced and directed by CustomerXPs and Banking Technology – narrate the tales of the fight between the forces of good (the Clari5 analytics and anti-fraud software) and the forces of evil. Based on real events and guaranteed to keep you on the edge of your seat!
May of the current year.

Her addiction was getting the better of her. “Absolutely Irresistible”, the new fragrance from Givenchy, was calling out to her. And those gorgeous Prada shoes had been winking at her from the shop front for the last three weeks.

“Man, I could kill for those.” “It’s been a while; I really need to find the dosh.” 

Georgina bit her lower lip with these thoughts swirling in her head like the steam from her coffee. She looked at the accounts’ list. Could she get a hold of one “dormant” account?

“Can Lady Luck please be kind? Am desperate, please!”

“Hey Georgina, how’s it going? Getting used to retail banking?”

“Hi Mark. Yeah, it’s different from corporate banking for sure. I miss the thrill of big numbers. That rush of working with millions instead of thousands. Ha ha ha.” 

“Hmm. So no new Gucci bag or a Marc Jacobs watch? The shops must be crying out for Your Shopaholic Majesty to give them time of day.”

“Mmm….yes, it’s been a while. Thanks for reminding me, must rectify that soon. He he.” 

Mark shrugs, gives a wry smile, a quizzical look and walks away.

She paused mid-way while taking a huge bite from her BLT sandwich. Her eyes widened. The $25,000 winked at her seductively. Money was her one and only love, her manna. She quickly hit her keyboard. Joshua Hamilton, checking account, “dormant”.

Was this her lucky day or what?

Georgina pushed her sandwich aside and quickly hit a few keys. “Active” flashed on her monitor. Joshua Hamilton was now “active”.

“Gucci, Prada, Jimmy Choo, here I come… yoo hoo!” Georgina thought to herself. A wicked smile, a faraway look and Georgina was revelling in the idea of big numbers. Her heart was thumping with excitement.

“It’s going to happen. Finally. I can sleep at night and don’t need any Xanax.”

Clari5 was rifling through the list of accounts doing its customary check. Sorting accounts by status, keeping a watchful eye on transactions by account holders and being its usual Poirot self – generally keeping an eagle eye on the safety and security of data, accounts, transactions and more.

Next, next, next, next, pause! Joshua Hamilton – active. Wait, hang on. Clari5 does an about take. Pause.

Quick flashback to April last year.

Joshua Hamilton was thrilled with life. It seemed to be going as per plan. New job, new city, new role, new life. Whoa!

He had to wind up his life in New York. Give up his apartment, sell his car, get rid of the furniture, among other things. But he decided to retain his bank account. Maybe it was for sentimental reasons, maybe it was just the idea of having monies in an account which he could use during emergencies, he didn’t close the account. He had $25,000 in that account. It felt good to have that kind of money.

His new firm thought it’d be ideal if Joshua opened a salary account with the bank they banked with. Apparently this bank had fantastic services – great paybacks on savings and good customer service as a local bank. Joshua thought why not, and opened a salary account with this new bank.

The $25,000 in his NY bank grew a little more, with interest etc. Zero transactions, zero withdrawals, zero anything. It was “dormant” but doing good.

Cut to present day.

Eyes follow her slow, shamefaced, hand-touching-chin movement out of the office as colleagues stare. Cops behind, cops in front. Her mascara is runny and covers her cheeks like ski tracks on Aspen.

Georgina bites her lips in regret. If only Clari5 hadn’t sounded the alarm, if only it wasn’t so darned smart, if only it didn’t keep track of every financial and non-financial transaction, she’d be wearing her Guccis today and looking like a million bucks. Even Xanax or Prozac wouldn’t be able to help her now, not in a prison cell for sure.

Damn Clari5!

When Joshua Hamilton’s “dormant” account status became “active”, it was instantly marked as suspect, when for over a year there were no transactions on his account.

When Georgina initiated a $10,000 encashment on this account using a withdrawal receipt forged with Joshua’s signature, Clari5’s real-time decisioning engine noted this.

The potential fraud transaction was blocked and generated an alert in the case management system.

And a case of deceit and willful defraudment is slapped on Georgina.

Episode 1: Malafide Intentions 

Episode 2: Blacklisted

Episode 4: Money Rolls

December 2016 Issue


Break-Filter-BubbleArticle: Blacklisted

Second in the new series of thrillers, co-produced & directed with Banking Technology narrates the fight between the forces of good (Clari5 analytics & anti-fraud software) and the forces of evil. Read More


NASSCOMInstant Charge Recovery with the Real-Time Tool That Top Banks Trust

Transform the tedious and error-prone manual charge recovery process in to a seamless, real time one with the combined power of Artificial Intelligence, Machine Learning, Analytics and Real Time Decisioning. Read More


ETPaper: Will EMV Standards Impact Fraud Control?

Has the global standard for card chip tech really been effective? This paper examines post-EMV trends of CNP fraud. Read More


ThreatCase Study: Real-time Cross-Channel Transaction Monitoring & Fraud Management for Top 5 Bank

Read how Clari5 delivered is delivering instant customer delight via intelligent, paperless digital branch banking for a prominent Indian bank. Read More


Staying ahead of the digital curve with real-time decisioning

Dynamics of digital

Financial institutions used to be the last candidates for change when it came to technology adoption. But over the recent past the banking sector has seen a dramatic ‘digital’ transformation given a discerning and demanding ‘digital’ generation, ferocious competition and a briskly evolving regulatory landscape.

From a customer’s perspective, a bank that has gone digital should be able to, at a minimum, instantly provide accurate information across devices, platforms and geographies. Customers are intolerant to service downtimes and want their needs addressed promptly and efficiently almost 24/7.

From credit cards to ATM to net banking to phone banking, the bank of today provides customers with an experience that is both seamless and of superior quality.

But banks can do a lot more to stay ahead of the ‘digital’ curve.

The digital bank of tomorrow

Many ‘progressive’ banks have gradually unified their entire IT ecosystem to harness the capabilities of big data analytics.

But there’s one more vital aspect banks must know – that they virtually have the customer’s ‘aatma’ or soul with them, given the behavioral intelligence and insights already resident across their multiple systems.

A bank is the only body that has the complete and in-depth lifestyle information of customers – earnings, spending, travel locations, home ownership status, marital status, right down to monthly fuel consumption.

With the variety and depth of insights available, banks can create instant, hyper-individualized interventions using a ‘segment of one’ approach to target customers precisely for intelligent cross-sell and up-sell.

So a unified, cross-channel digital strategy that utilizes this ‘soul’ to deliver an exceptionally superior customer experience becomes essential. Combine this with real-time technology, and banks have a compelling value proposition.

The soul of true digital transformation

The soul analogy also applies perfectly in combating sophisticated financial fraud, where deviations and discrepancies can be detected and resolved ‘intelligently’ in the blink of an eye.

Given the customer insights available, the same real-time decisioning can be leveraged to instantly detect anomalies and prevent them from occurring.

A meaningful digital transformation must include the customers’ soul. The digital bank of tomorrow must articulate a strategic platform that goes beyond servicing customers flawlessly and have intelligent revenue maximization and fraud detection capabilities.

Fraud-proofing Credit Cards Intelligently

While credit cards have transformed purchase transactions, it has not been without simultaneously growing vulnerabilities.

Financial fraud losses across payment cards, remote banking and cheques totalled £755 million in 2015 – a 26% jump when compared to 2014 says Financial Fraud Action UK.

It says that the rise across all fraud loss types during 2015 owes much to the growth of impersonation and deception scams, as well as sophisticated online attacks such as malware and data breaches.

Of the prevalent card-frauds, card-not-present (CNP) and payment fraud, CNP (where the card holder needn’t be present online or phone for the transaction) is the dominant form of card fraud in Europe in addition to the UK.

Payment fraud not only involves falsely creating or diverting payments; it goes to the extent of creating false accounts and scamming on a large scale. A merchant account created for a seemingly genuine organization performs transactions through the stolen credit cards.

The UK tops the highest jump in credit card fraud in Europe with an 18 percent rise resulting in £ 88 million of losses.

Increased rate of personal data compromise through data breaches was one likely cause for the jump.

Credit Cards Theft Concept. Hacker with Credit Cards on His Laptop Using Them For Unauthorized Shopping. Unauthorized Payments

Globalization and technology driving credit card fraud

The ability to contain scams is challenging given globalization. With financial organizations spreading their wings across geographies, the ‘law-of-the-land’ comes in to focus.

Each country has specific policies and laws that banks have to abide by leading to a lack of a common security cover. This leads to vulnerabilities let alone the effort involved in understanding laws, creating policies and maintaining them.

Hi-tech card fraudsters rely on technology as they look for ways to compromise customers’ personal and financial details and use that to commit frauds.

They hack into systems, run random generated bank account numbers and sometimes approach as legitimate organizations and lure information under the pretext of seeking data via email, text messages and phone calls made to seem as if they are from tax departments with threats of deportation or imprisonment.

Enter EMV and NFC

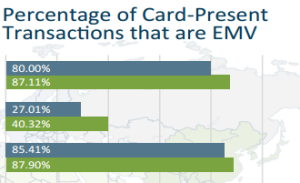
Europe was one of the early adopters of EMV (Europay, MasterCard, Visa) – a global security standard for chip-cards and the technology used to authenticate chip-card transactions.

EMV helps when the physical card is required for a transaction, protects from counterfeiting, CNP fraud continues to thrive. View the stats.

A CNN Money report features a claim by a security company having discovered a way of rewriting magnetic chip code to make it look like a chip-less card. This takes it back to the basic fraud technique of counterfeiting.

NFC allows smartphones and other devices to communicate with each other when they’re physically very close. NFC can also be present in wearable devices.

NFC has gained some movement in the US and is now being launched in Europe. According to Markets & Markets, the NFC market is expected to touch $22 billion by 2020.

While the technological advancements are definitely encouraging, they point to a fundamental question on fraud-free credit card transactions – can a channel centric (in this case, credit card only) approach be a fool-proof solution?

E-commerce.

Solutions must rely on ‘absolute real time cross-channel intel’

While card security technology has evolved from signature cards to chip-and-pin cards and now to NFC, they will deter sophisticated, hi-tech fraudsters from inventing newer techniques in staying a step ahead.

Anti-fraud solutions cannot merely rely on a channel-centric approach. They will have to rely on advanced technologies that harness the collective wisdom about customers (factual and behavioural) already resident across a bank’s systems, pull the collective cross-channel insights at lightning speed from all channels to detect and thwart fraud intelligently in absolute real-time even as the fraud is being committed.

This gives banks an edge over fraudsters because channel-specific fraud relies only on breaching that particularly channel’s (credit cards) data.

If banks are in the know of suspect transactions while it is in progress, they can prevent the fraud from being committed in the first place instead of taking action post-incident when the deed is done.

Absolute real time anti-fraud technology coupled with continuous monitoring, stringent regulatory compliance and improved auditing are some of the primary measures banks must adopt to stay ahead of evolving fraud technology.

SWIFT Codes Under Attack: How Safe Are Banks?

Gone are the days when ski-masked felons would barge into banks with guns cocked and order everyone to get down. With the internet becoming ubiquitous and as banks and technology have evolved, so has financial crime.

The modern scarfaces operate from the comfort of an undetectable pad half way across the world. They are high IQ, tech-savvy and their only weapons are their brains and their gadgets. Global technological advancements and online anonymity have in fact come as a blessing for the intelligent ‘digital’ felon.

Though banks have grown in leaps and bounds from a business standpoint, there is still the question of how shielded they really are from hacking, money-laundering, asset siphoning, etc., all of which have become alarmingly regular.

So, what have banks been doing to combat the situation? To start with, they implemented measures to mitigate these risks and are regularly evaluating their security systems. One such measure was the implementation of the SWIFT codes. But, the question is, is it enough?


What is a SWIFT Code?

Society for Worldwide Interbank Financial Telecommunication codes or SWIFT Codes, also known as Bank Identifier Codes (BIC) are unique identification codes allocated to each bank. These codes are used when transferring money between banks, especially for international wire transfers and for communication between banks.

Currently, there are about 40,000 ‘live’ SWIFT Codes (those which are actively connected to the SWIFT network) and about 50,000 ‘passive’ SWIFT Codes (used for manual transactions).

Is the SWIFT Code mechanism helping? It was, until the recent (February 2016), high-profile scandal where USD 81 million was stolen from a bank in Bangladesh, came to light. The incident highlighted the insufficiency of SWIFT Codes in securing online banking transactions and how instances of cybercrimes against SWIFT member banks have been increasing.

Few other examples of such heists which occurred through SWIFT manipulation:

  • Banco del Austro (Ecuador)  – a whopping USD 12 million
  • Tien Phong Bank (Vietnam) – a mere USD 1.36 million

Banks or SWIFT – where does the onus lie?

While SWIFT defended itself by stating that the network itself wasn’t attacked during any of the above mentioned heists, these attacks, however, are disconcerting and reflect upon the vulnerabilities of the system run by SWIFT.

Leonard Schrank, Chief Executive at SWIFT for 15 years, suggested that SWIFT develop an anomaly detector to catch dubious message traffic as it arrives. He believes that the network had long since known that end-users are a key vulnerability and that SWIFT needs to work harder to alleviate these attacks.

That being said, the onus lies on every single bank to ensure their own security first so that systems are not susceptible to attacks and threats. This cannot be achieved by depending on SWIFT alone. Banks will need to take the extra step to secure their systems and increase security controls.

How is SWIFT working towards better security protocols?

Since the Bangladesh bank drama, SWIFT has been urging its member banks to beef up their security measures and has promised new rules to improve security for bank transfers. In line with this, SWIFT sent a communication to all its users in May 2016 updating them on the steps they were taking to provide better security, including:

  • Information sharing – SWIFT will continue to notify all member banks, as soon as possible, of any cases of malware that is made known to them and update the banks with all new and relevant information related to cybercrimes. To improve this information sharing, SWIFT will centralize all new and existing information in their Knowledge Base in a restricted customer section on SWIFT.com
  • Collaboration against cyber threats – the banking fraternity’s security can only be achieved through a collaborative approach between and among SWIFT, its users, its central bank overseers and third party suppliers. To this end, all of them need to inform SWIFT of any suspected fraudulent use of their institution’s SWIFT connectivity or related to SWIFT products and services immediately.

What else can banks do?

To begin with – putting the house in order. Banks need to start identifying the challenges they face. Some of them would be:

  • identify risks within the AML processes
  • study how to bring in agility in their AML strategy
  • ensure detection and investigation of suspicious activities
  • ensure AML operations’ team is equipped with intelligent real-time, cross-channel tools

There’s a variety of anti-fraud technology solutions available, but banks must realize that strategies that delivers real-time, actionable intelligence is increasingly becoming the de-facto standard, given the innovation in sophisticated fraud. Financial institutions need solutions that can help automate, streamline and comply with existing and emerging regulatory AML/CFT compliance programs and solve these problems in real time.

Innovative solutions are now available that monitor and detect suspicious transactions across channels and in real- time as it happens, helping the bank’s risk and compliance teams take accurate decisions at the precise right time. These solutions feature Suspicious Activity Monitoring, Customer Risk Categorization, Entity Identity Resolution / Watch List Filtering, Regulatory Reporting (CTR/STR/SAR), Case Management and Entity Link Analysis.

While financial institutions, networks such as SWIFT, regulators and policy makers are aware of the systemic gaps, radically more stringent lines of defence will be the shape of things to come. Heists, laundering and other frauds will continue to occur as hackers get more brazen, but the least banks can do is have foresight on the magnitude of the problem and take sure steps to secure themselves.

As Malcolm Marshall, KPMG’s Global Head of Information Protection & Business Resilience states, “Security is not something that should get in the way of doing business but is something that enables you to do it more safely. Hopefully that means something to you and your customers.”


Episode 1: Malafide Intentions​

Our new series of thrillers – produced and directed by CustomerXPs and Banking Technology – narrate the tales of the fight between the forces of good (the Clari5 analytics and anti-fraud software) and the forces of evil. Based on real events and guaranteed to keep you on the edge of your seat!

The alert flashes on the dark screen. His cat nap is disturbed by the “on/off” flashing on the monitor which causes his eyelids to flutter open. He looks at the array of numbers and text that appear to be just a vast, random set of data, for the lay person. But Oliver’s trained eye and keen mind are attuned to pick out anomalies from this data load. Oliver wasn’t called Hawk by his colleagues, the keenest, sharpest AFO (anti-fraud officer) at the Bank of Sentee (BoS) for nothing.

Oliver’s eyes rapidly scan through Michael Hook’s transaction history.

POS 12.30 pm SF, 22.07.16, Starbks
POS 16.30 pm SF, 22.07.16, Movtkts
POS 19.30 pm SF, 22.07.16, Metreon
POS 20.20 pm ABJ, 22.07.16, Fouani Electronics
 – there it was, popping out at him like a girl in a magenta halter in a room full of black tuxedos! Oliver quickly runs a check for country codes and finds ABJ is Abuja, Nigeria.

Oliver’s fingers flew over the keyboard and his eyes scanned through Michael Hook’s transaction history for the past seven days. Come on Clari5, he urged. Clari5, Oliver’s best friend, obliged. Michael Hook’s transactions seemed fine, no anomaly, no suspicious activity. So then what explained Nigeria?

Could Michael, a regular graphic designer, travel from San Francisco to Nigeria, a distance of over 7700 miles in 50 minutes? He ain’t no Superman!

12.30 pm, 22.07.2016, Starbucks, 3595 California Street, San Francisco

“Good afternoon sir, can I take your order?”

“Hi. Mmm… I’ll have a chicken BLT sandwich and a decaf Pike Place coffee, please.”

“Sure. What name shall I add to the order?”

“Michael Hook.”

“Have a seat and we’ll call out your name. Have a good day.”

Michael looked at his Fitbit. 12.33 pm. God! “Is it stuck or is it me?” he wondered. He looked thoughtful as he sat down, his mind unspooling the conversation he had with Jessica in the morning. Sigh! He swiped through his messages. “4.30 show, don’t forget, J.” Her curt response: “Yup.”

He’s got to make it up to her, he loves her too much to lose her. Thoughts swirled in his head like the steam from the coffee mug. Should he buy her something before the movie? A ring? Would she accept?

“Can I afford to get married?”

Technology is a savior. Michael checked his bank account on his smartphone. $10,578. He had the dosh. He felt a sliver of excitement welling up inside of him. Yes, maybe he would surprise Jessica after all. 

16.30 pm, 22.07.2016

Back in office Michael bought two movie tickets at movietickets.com. “Booked for To Steal From A Thief. See you at 6.00 – AMC Metreon,” he texted. “See you” popped up on his phone. Michael continued to look at his text message knowing Jessica was still miffed at him, but his modus operandi was all sorted.

POS 19.30 pm SF, 22.07.16

“Large tub of cheese popcorn and two Diet Cokes, please!”

“That’ll be $5.50. Thank you.”

The counter assistant at the popcorn counter at the Metreon swiped Michael’s card. It’s intermission and Michael wanted to hurry back to Jessica. She seemed to be enjoying the movie. He knew it was all going to be okay.

POS 20.20 pm ABJ, 22.07.16, Fouani Electronics

“Come on Michael,” Oliver muttered under his breath. “Tell me you’re in San Francisco buddy and we’ll be fine, just confirm it man.” But Michael’s phone was on “silent”. He missed the SMS alert completely, and the second one as well.

“Breathe Oliver, it’s okay Oliver, have sent the two alerts to Michael Hook.” Oliver tried to soothe his frayed nerves. All POS transactions checked out. The last one at 20.20 ABJ seemed different. Was Michael in Nigeria? But Michael hadn’t travelled anywhere in the last 12 months! Clari5 confirmed that. Oliver commanded Clari5 to give up Michael’s transaction history for the last six months to double-check. No, nothing. Michael wasn’t a big spender. And neither was he a defaulter. His last big electronics purchase was for a Kindle. Wow!

Oliver checked with Clari5: “do you think it’s a fraudulent transaction?” Clari5 advised Oliver to refuse authorisation of Michael’s card for $2,150 at Fouani Electronics, ABJ. That’s it, Oliver made his decision. He ran a few commands and an SMS was sent to Michael disabling his credit card.

22.00 pm, 22.07.16

Michael looked at the two texts from BoS. His credit card was disabled. At that exact moment his phone rang. “Oliver Pagliace from BoS. Am I speaking with Michael Hook?” 

Two days later at Fiore d’Italia – 20.00 hrs.

“OMG! Really? Oh darling, when did you, I can’t imagine…”

Michael just finished proposing to Jessica. With his credit card.

22.00 hrs, BoS branch, San Francisco, California – 24.07.16

The light from the monitor was blinking. Oliver was just biting into a sandwich. He turned around. Clari5 was at it again. This time it was Dar-es-Salaam.

“Gotcha.”

Episode 2: Blacklisted 

Episode 3: Inside Job

Episode 4: Money Rolls
Financial Mecca Tightening The Screws On Anti-Money Laundering!

“Breaking News: Singapore to use data tracking against money-laundering”. What bearing does this headline have on a safer and more secure banking system?

The 1MDB fiasco

Let’s rewind to 2015 and 1Malaysian Development Berhad – a Malaysian fund set up in 2009 by the Prime Minister of Malaysia, with the intention of turning Kuala Lumpur into a financial hub, much like its neighbour, through strategic investments, to help boost the economy.
The Wall Street Journal broke a story in 2015 and reported a paper trail of alleged misappropriation of funds in 1MDB to the tune of US $ 700 million, traced to the PM’s personal accounts.

All hell broke loose and investigations by the US Department of Justice revealed that the quantum of laundered money is actually US $3.5 billion!

Since then, multiple foreign authorities have been involved in the investigations of this scam – something so massive that it has thrown open a Pandora’s box on the prevalent AML security systems in banks.

In May, earlier this year, Singapore, South East Asia’s leading financial centre ordered the Swiss bank BSI to shut down on charges of “suspected corruption of public foreign officials, dishonest management of public interests and money laundering”.

MAS (Monetary Authority of Singapore) and its role in banking regulations

A brief perspective on MAS and its scope of authority – www.mas.gov.sg states, “As Singapore’s central bank, the Monetary Authority of Singapore (MAS) promotes sustained, non-inflationary economic growth through appropriate monetary policy formulation and close macroeconomic surveillance of emerging trends and potential vulnerabilities.”
“It manages Singapore’s exchange rate, foreign reserves and liquidity in the banking sector. MAS is also an integrated supervisor overseeing all financial institutions in Singapore — banks, insurers, capital market intermediaries, financial advisors, and the stock exchange. “


“With its mandate to foster a sound and progressive financial services sector in Singapore, MAS also helps shape Singapore’s financial industry by promoting a strong corporate governance framework and close adherence to international accounting standards.”

“In addition, it spearheads retail investor education.”

“MAS ensures that Singapore’s financial industry remains vibrant, dynamic and competitive by working closely with other government agencies and financial institutions to develop and promote Singapore as a regional and international financial centre.”

“Given the nature of its position and authority, one of its functions is to “conduct integrated supervision of financial services and financial stability surveillance.”

“Moreover with Singapore being a key financial mecca in the South Asian region, it plays an active role in international fora and is a key contributor to shaping financial regulatory norms.”

In this context, given the nature of the 1MDB scandal, Singapore’s MAS has been probing different banks for any breach of security and money laundering activities while handling transactions linked to 1MDB.

To quote a report in Shanghai Daily, “The Monetary Authority of Singapore is looking at several aspects of the UBS and DBS Group Holdings’ operations including whether they were diligent enough in knowing who their customers were and what the source of their funds was, and whether they were particularly careful in screening politically-exposed persons such as government officials, banking and legal.”

The investigation by MAS could lead to hefty fines and various other penalties if the banks under question were found to be non-compliant with the very stringent anti-money laundering rules, policies and measures.

In the past, the US has imposed hefty penalties on banks found to have lapses with money-laundering activities, tax evasion and international sanctions, but Asian regulators have found to be slow to act.

Given this context, it was incumbent upon Singapore to act tough and prove that banks in the city-state are complying with anti-money-laundering rules.

Given this back story it is but natural for the central bank of Singapore to clamp down heavily on any fraudulent activity that jeopardizes the reputation of Singapore as a mecca for banking not only in Asia but globally.

“We will make more robust risk assessments of financial institutions’ business activities, client profiles, geographical connections, transaction volumes and quality of controls,” Ravi Menon, the MD of MAS said.

According to the UN Office on Drugs and Crime, the estimated amount of money siphoned off globally in one year is 2 – 5% of global GDP, or $800 billion – $2 trillion in current US dollars. Money laundering is an epidemic and must be curbed – no question about it.

Advanced tech to the rescue

With escalating frequency and complexity of financial crimes, it is imperative for banks to pay greater attention to fraud prevention not just from a regulatory compliance perspective but for better operational risk management.

They must understand that if their systems are not preemptive in nature, then ‘post-incident’ scenarios are going to be quite common.

Banks need to work in partnership with solution innovators to combat the menace.


Given the sophistication of large-scale economic fraud., there is a need to move away from conventional channel-centric AML approaches and consider real-time, cross-channel solutions that have the capability to analyse big data and provide real-time intelligence covering Suspicious Activity Monitoring, Customer Risk Categorization, Entity Identity Resolution/Watch List Filtering, Regulatory Reporting (CTR/STR/SAR), Case Management and Entity Link Analysis.

Banks must understand the gravity of the situation and begin evaluating solutions that can quickly enable a strong and strategic fraud prevention framework to pro-actively thwart potential threats from sophisticated money-laundering syndicates.

Sources: